
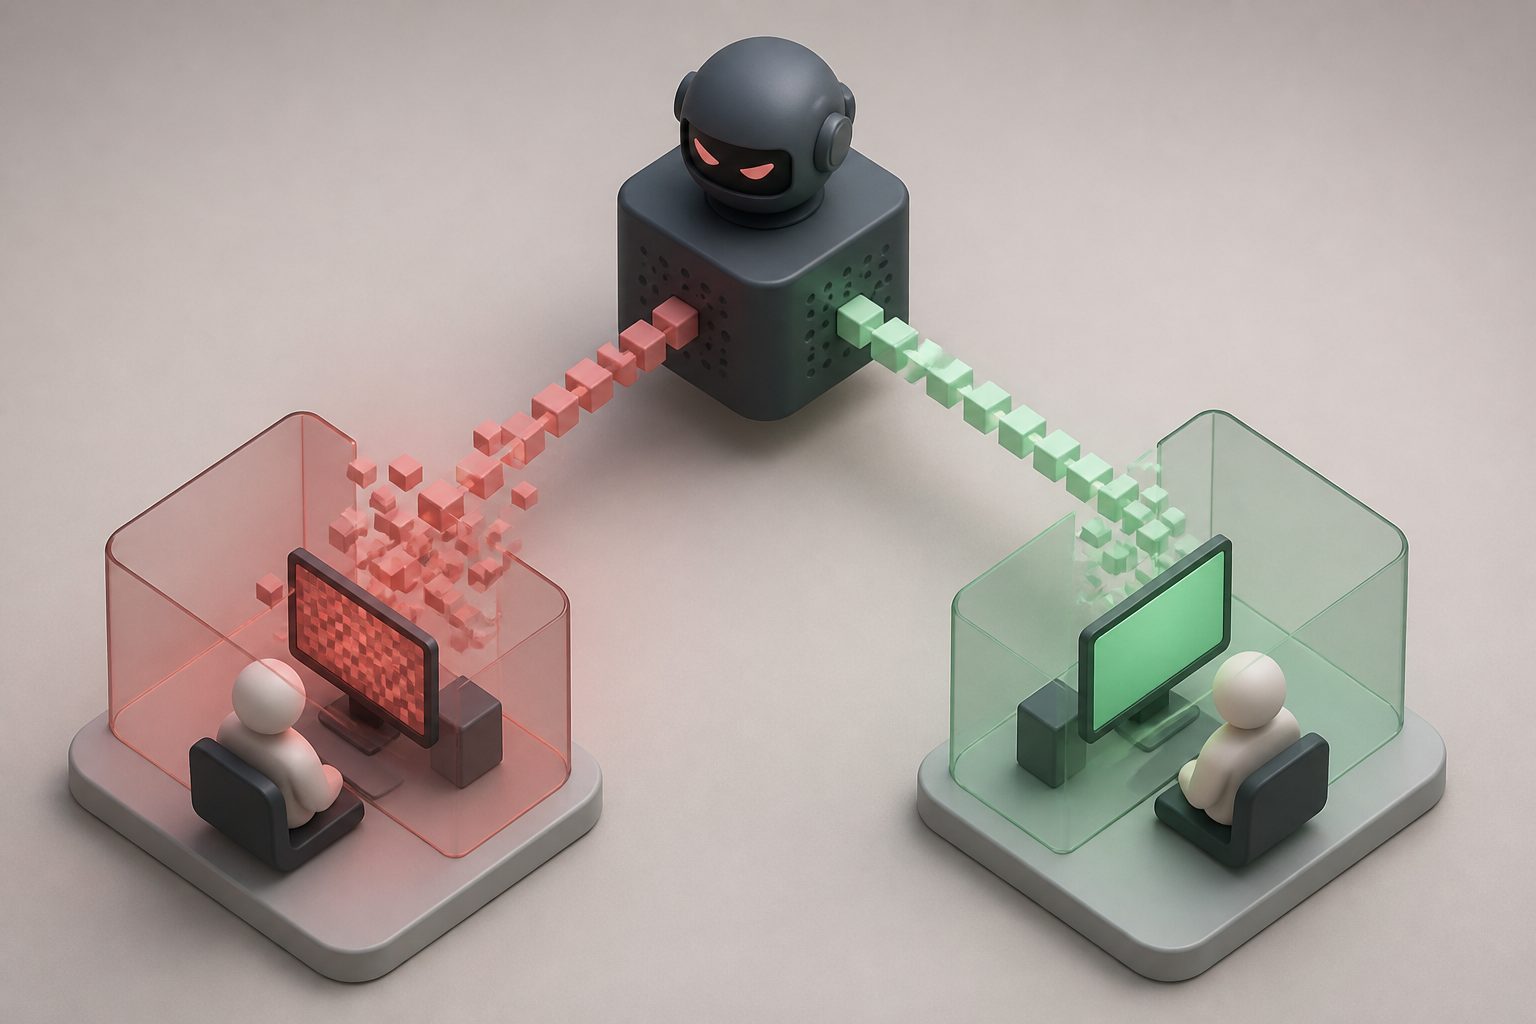
An AI attack can fool one client's system while sparing another
Researchers describe an attack on personalized federated-learning systems that aims to fool selected client models without disrupting designated “friend” models. In the main test setup, it succeeded against at least 88% of target cases while preserving at least 81% accuracy on friend models, though performance varied with the information available to the attacker.
·80 views